Atomicwork’s Access Ops Manager: Check What Happens After a Denial
Atomicwork’s Access Ops Manager is positioned around access requests and provisioning, which makes one verification question especially important: after a request is denied, what actually changed? In enterprise identity operations, the safest way to answer that question is not to rely on a ticket note or a status message alone, but to confirm the resulting account state and audit trail directly.
Atomicwork’s Nov. 6 release says the company launched an AI coworker marketplace for enterprise IT and security and introduced six prebuilt IT coworkers. In its companion blog post on certified AI coworkers, Atomicwork describes certification as its own process that includes integration and skills review plus role-specific evaluations. That framing is useful context: certification and workflow outcomes are related, but they are not the same thing, and access decisions still need operational verification.
A harmless sandbox test with dummy accounts
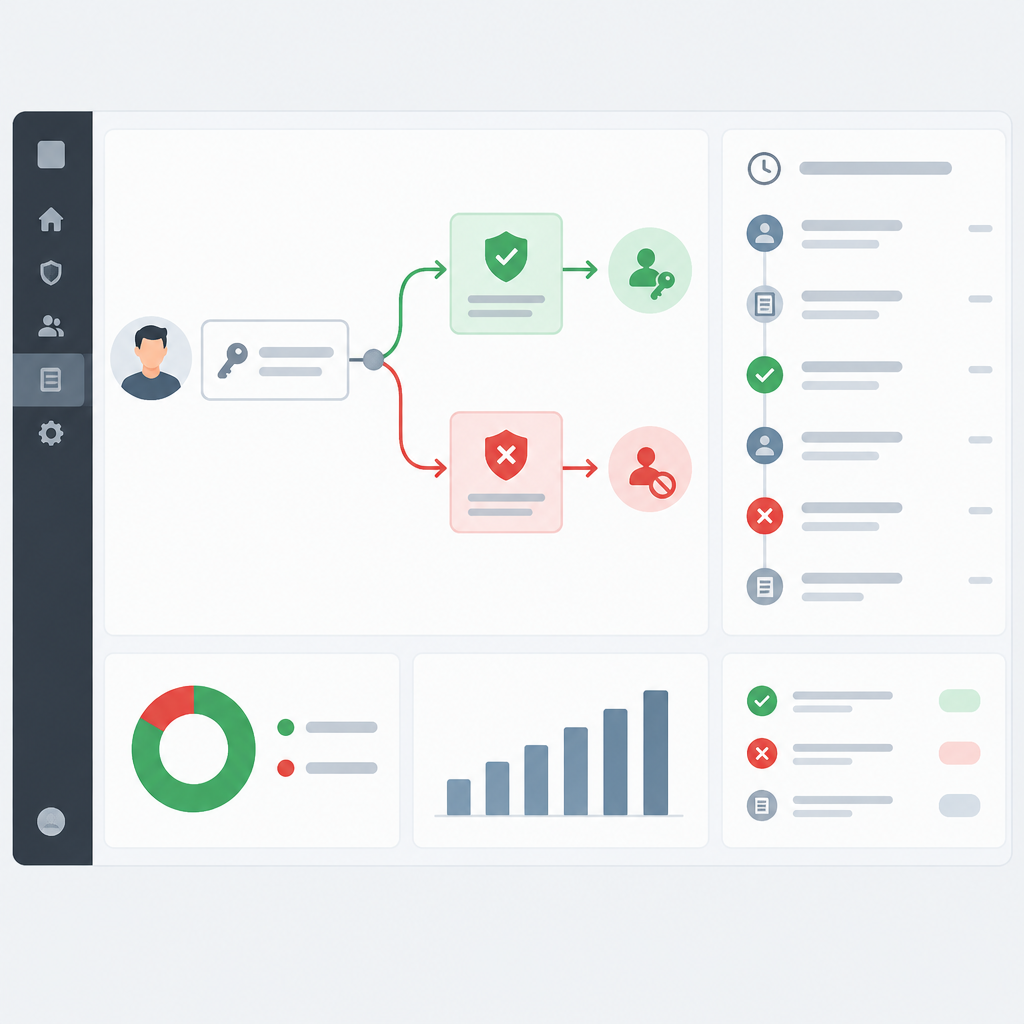
A simple, hypothetical test can be run in a non-production sandbox with dummy users and a harmless group such as “Sandbox-Access-Review.” Use one approved request and one denied request. After each request is processed, check the actual group membership and the audit record. Look for timestamps, the request ID, the decision outcome, and the final membership state. The key point is that the denied case should leave membership unchanged.
- Approved request: confirm the dummy account is added to the sandbox group, and that the audit trail shows the request ID, approval outcome, and timestamp.
- Denied request: confirm the dummy account is not added to the group, and that the audit trail shows the denial outcome without any membership change.
- Evidence check: treat the ticket message as informational only; use the directory or access system record as the source of truth.
If you want an optional third scenario, a pending approval case can be used as a proposed test only. In that state, the expected result is still no membership change until a real approval is recorded. This can help distinguish “waiting” from “approved” and “denied” in reports or dashboards.
For teams evaluating access operations workflows, the lesson is straightforward: validate what the identity system actually did, not just what the request thread says happened. That discipline is especially important when testing denial paths, where the correct outcome is often the absence of change.
Sources
Atomicwork blog: Certified AI coworkers
PR Newswire: Atomicwork launches AI coworker marketplace for enterprise IT and security