What changed in Cloudflare SAML discovery
Cloudflare's November 18, 2026 release adds signing-certificate discovery from an IdP metadata URL. The endpoint must serve SAML XML directly over public HTTPS without authentication or redirects; JWKS is not supported. Access caches certificates rather than polling the endpoint. Removing a certificate from metadata therefore does not immediately remove cached trust or revoke existing Access sessions.
Why removing metadata is not immediate revocation
Cloudflare's setup guide calls for one EntityDescriptor with an entityID matching the configured issuer. Choose metadata_url or manual signing certificates, not both, and preserve unrelated IdP settings. For a planned change, publish old and new certificates before switching the signing key; allow retrieval time and retain the old certificate for in-flight responses and rollback.
Emergency replacement is different: re-saving unchanged settings does not force a refresh. Cloudflare directs an authorized administrator to switch to manual certificates with only a trusted replacement. Existing sessions and application tokens require separate revocation when responding to compromise. Signing-certificate discovery does not rotate Access assertion-encryption certificates.
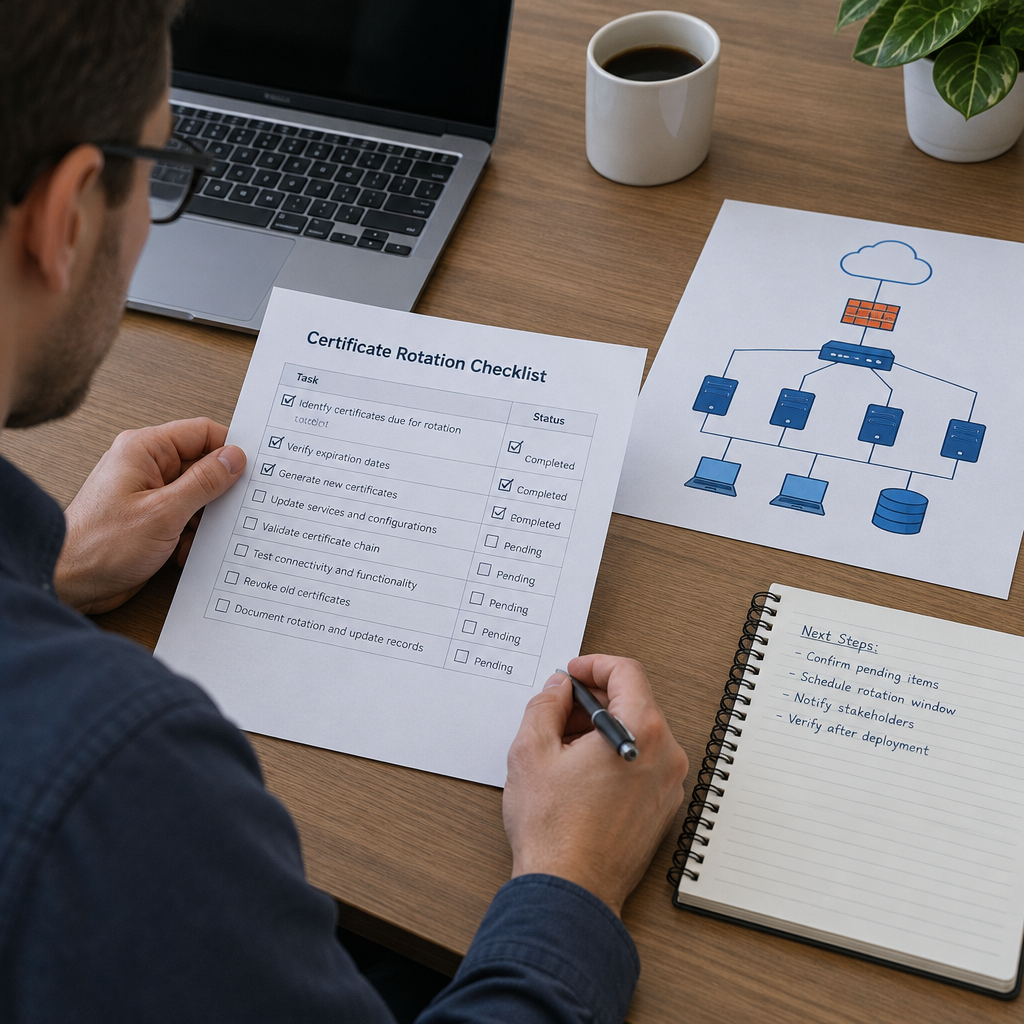
A local tabletop review record you can use
- Published metadata: record the approved URL, observation time and certificate fingerprints reviewed by the change owner.
- New login evidence: plan approved nonproduction positive and negative checks; record actual outcomes only after running them. These are proposed checks, not tests performed for this article.
- Session disposition: keep a separate field for the owner's session/token response decision and evidence of any completed action.
- Ownership: name the IdP and Access reviewers, change window and rollback decision. An unchecked box should remain visibly unresolved.
A simple example to document, not a live test claim
Hypothetical example: a change record has three sections. The IdP owner completes the publication section, while login evidence and session disposition are still blank. The reviewer keeps the change open. A completed publication row is useful evidence for that row only; it does not stand in for an observed login result or a completed session response. This is an illustrative review method, not a live test or a claim about a particular deployment.
Operational takeaway
Before declaring success, ask which observation supports each completed field. A URL and a successful sign-in answer different questions. Record what was actually checked, who checked it, and what remains unresolved. Coordinate any production change through the authorized owners and current product guidance; a local checklist cannot reveal a service's internal cache.
Cloudflare changelog: SAML IdP certificate discovery (Nov 18, 2026)
Cloudflare docs: Discover IdP signing certificates